Security Guide
Goal: Protect your data and manage access securely.
Security Architecture
| Layer | Protection |
|---|---|
| Network | HTTPS everywhere, TLS 1.3 |
| Authentication | Azure AD B2C, SSO, MFA |
| Authorization | Role-based access control |
| Data | Encryption at rest and in transit |
| Audit | Every action logged |
Key Security Features
1. Connection Security
- All data connections use encrypted protocols
- Credentials stored in Azure Key Vault
- Connection strings never exposed in UI
2. API Security
- JWT tokens with configurable expiry
- Rate limiting per token
- Scope-limited access
3. Audit Trail
- Who did what, when
- Immutable logs
- Export for compliance
Governance isn't optional. Every query, every change, every API call is tracked and attributable.
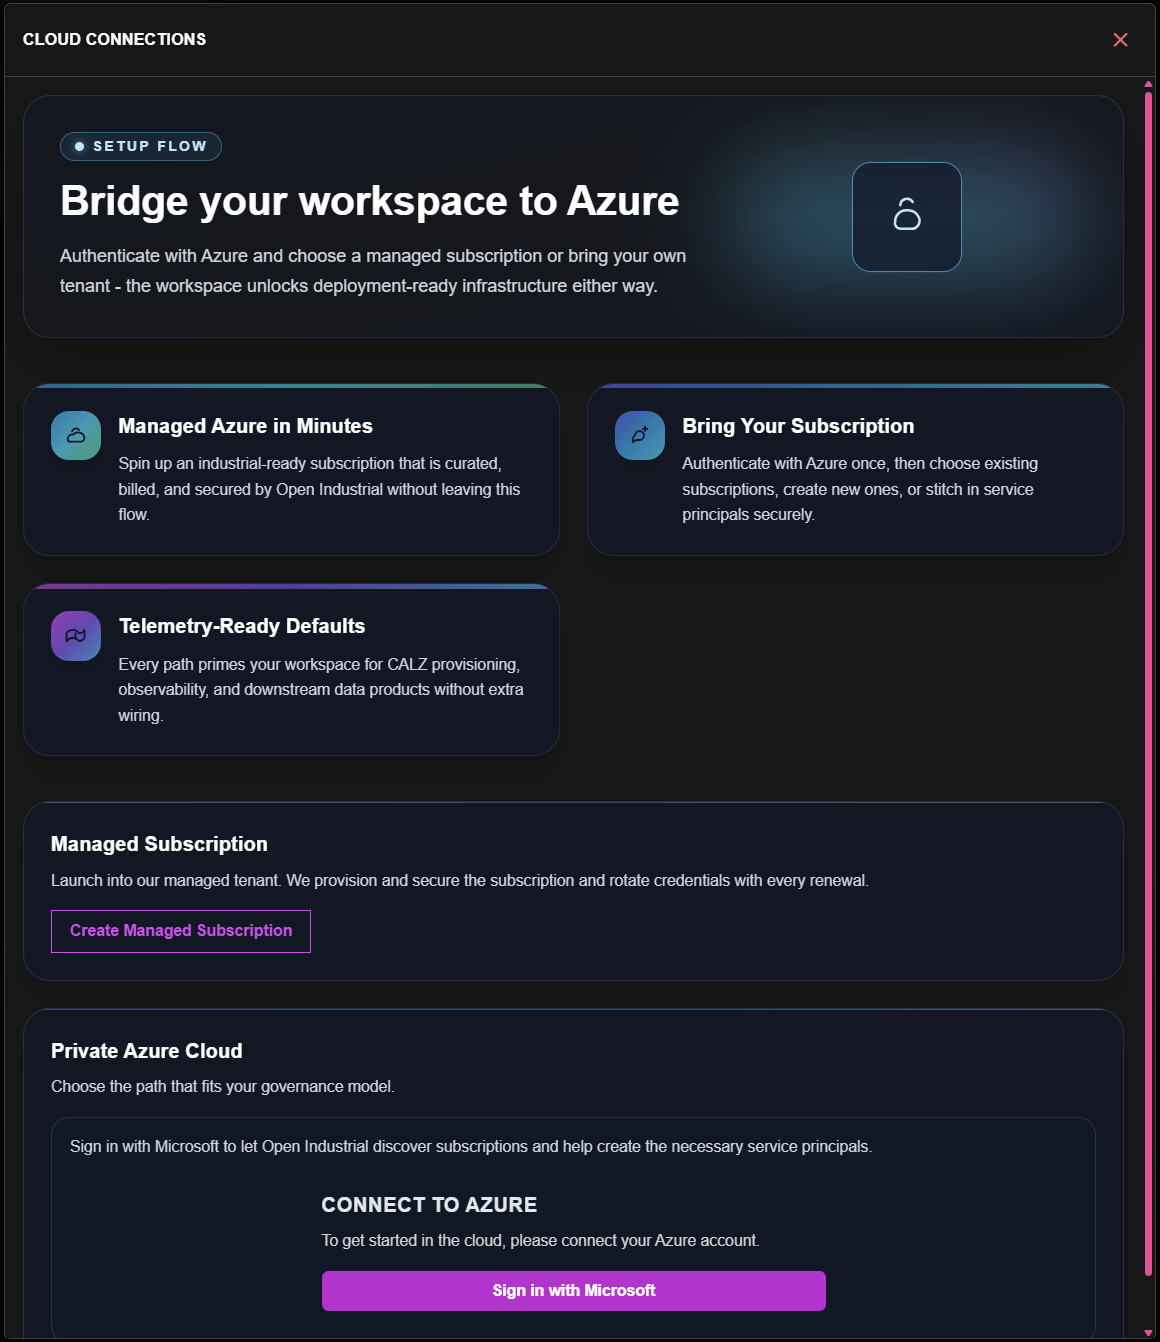
Private Cloud Security
When deployed to your infrastructure:
| Aspect | Your Control |
|---|---|
| Network | Your VNet, your firewall rules |
| Identity | Your Azure AD tenant |
| Data | Never leaves your boundary |
| Compliance | Your certifications |
Common Security Tasks
| Task | Guide |
|---|---|
| Create API keys | Secrets Management → |
| Configure JWT expiry | Secrets Management → |
| Review audit logs | User Management → |
| Manage team access | Permissions → |
Compliance
| Standard | Status |
|---|---|
| SOC 2 Type II | In progress |
| GDPR | Compliant |
| HIPAA | BAA available (Enterprise) |
Next Steps
| If you want to... | Go to... |
|---|---|
| Manage API credentials | Secrets → |
| Control team access | Permissions → |
| Understand audit system | User Management → |